

This wasn’t just another Patch Tuesday… it was yet another signal.
Another signal that the traditional model of “patch the OS and you’re covered” is officially outdated. This cycle brought a convergence of critical Windows vulnerabilities, actively exploited flaws, and high-risk browser issues, all showcasing how your biggest risk is now sitting inside your users’ browsers.
Some of The Most Critical & Impactful CVEs (April Patch Cycle)
Here are some of the vulnerabilities that stood out to me… not just by severity, but by how they can be chained together in real-world attacks.
–> Actively Exploited (Zero-Day / In-the-Wild)
CVE-2026-29901 – Windows Elevation of Privilege (CLFS Driver)
- Type: Elevation of Privilege
- Impact: SYSTEM-level access
- Status: Actively exploited in the wild
This is a classic post-exploitation weapon. Once an attacker lands any foothold (phishing, browser exploit, etc.), this vulnerability gives them full control of the system.
This is how ransomware operators turn “one click” into full domain compromise.
CVE-2026-29912 – Windows Win32 Kernel Elevation of Privilege
- Type: Elevation of Privilege
- Impact: Kernel-level execution
- Status: Observed exploitation activity
Often paired with browser or document-based exploits to break out of user-mode restrictions.
–> Remote Code Execution (The Initial Entry Point)
CVE-2026-29877 – Windows MSHTML Platform RCE
- Type: Remote Code Execution
- Vector: Malicious web content / document preview
- Affected Component: Legacy IE rendering engine still used by apps
Why this is dangerous…
- Doesn’t require users to “open” anything traditionally
- Can be triggered through preview panes, embedded web views, and Office documents
A quiet entry point that is perfect for targeted attacks.
CVE-2026-29854 – Windows OLE Remote Code Execution
- Type: RCE
- Vector: Malicious Office documents
Attack chain example–>
- User opens document
- Code executes silently
- Attacker pivots using EoP vulnerability
This remains one of the most reliable phishing-to-compromise paths.
–> Browser & Chromium-Based Threats
Google Chrome and Chromium-based browsers saw multiple high-severity patches tied to memory corruption and sandbox escape vulnerabilities.


CVE-2026-3156 – Chrome Use-After-Free Vulnerability
- Type: Memory corruption
- Impact: Potential RCE
- Attack vector: Malicious website
CVE-2026-3159 – Chrome Sandbox Escape
- Type: Security bypass
- Impact: Escape browser isolation
Why Do These Matter Together?
The attack chain now looks like this…
- User visits malicious site
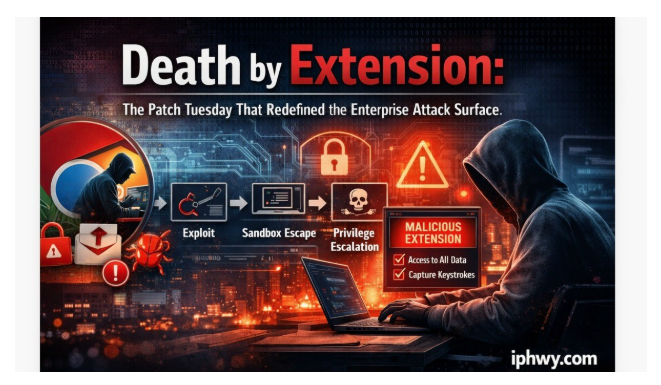
- Browser exploit (Chrome CVE) triggers code execution
- Sandbox escape allows OS-level interaction
- Windows EoP (like CVE-2026-29901) grants SYSTEM access
No phishing email or attachment required. Just a browser session.
Oh My! Those Browser Extensions…
- Run with persistent privileges
- Often have access to all web traffic, session cookies, and authentication tokens

Most organizations don’t audit them, restrict them, or even monitor them!
Meanwhile, a compromised or malicious extension can bypass EDR visibility, network controls, and traditional logging. In many cases, it becomes a silent insider threat installed by the user themselves.
This patch tuesday hilighted how this wasn’t about individual vulnerabilities. It exposed a repeatable, reliable attack pattern …
Browser → Execution → Escape → Escalation → Control
And every step in that chain had a critical patch this month.
Do This!
1. Prioritize Exploit Chains, Not Just CVSS Scores
A “moderate” browser bug + a “moderate” EoP = critical breach
2. Control the Browser Layer
- Enforce updates aggressively
- Standardize browser versions
- Monitor deviations
3. Implement Extension Governance
- Allowlist only approved extensions
- Block unknown installs
- Audit permissions regularly
4. Correlate Browser + Endpoint Telemetry
SIEMs should be able to answer… what site was visited, what process spawned, and what privilege change followed?
5. Assume Initial Access Is Easy
Focus defenses on containment, detection, and privilege boundaries
We’ve spent years hardening firewalls, servers, and endpoints. But this Patch Tuesday made one thing clear… The modern attack surface lives inside the browser, and most organizations aren’t defending it.
The most recent ‘Patch Tuesday’ didn’t just fix vulnerabilities, it exposed where many are still blind. If you’re not managing browser risk nowadays, you’re not managing risk at all.