

Most executives don’t lose sleep over cybersecurity tools. They lose sleep over margins.
Revenue growth. Market expansion. Operational efficiency. Customer retention. Acquisition strategy. EBITDA.
That’s precisely why cybersecurity often gets placed into the wrong business category. It’s frequently viewed as operational overhead… somewhere between insurance renewals, software licensing, compliance requirements, and unavoidable IT expenses. For many leadership teams, cybersecurity remains something to minimize rather than strategically evaluate. And that mindset is becoming increasingly expensive.
The biggest cybersecurity costs rarely begin with a ransomware headline splashed across national news. They usually begin much more quietly –>
- A delayed infrastructure refresh because “the systems still work.”
- An identity modernization project pushed into next year’s budget.
- Backup improvements postponed because there are “more urgent priorities.”
- Documentation projects deferred because they don’t appear revenue-generating.
- An aging platform remains untouched because replacing it feels expensive.
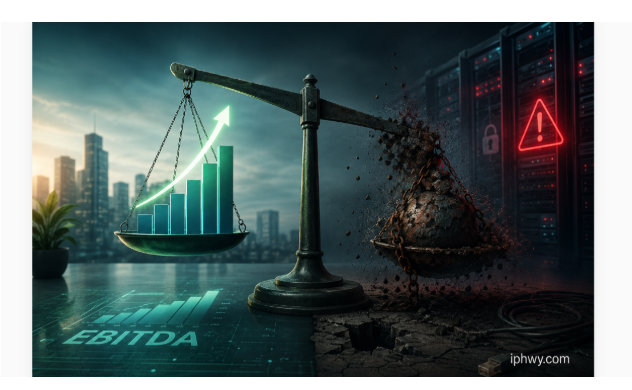
Individually, each decision can seem financially responsible. Collectively, they often create a slow and nearly invisible drain on EBITDA. And by the time executives recognize the impact, the financial damage has often been compounding for years.
Years ago, manufacturing executives understood this concept well.
If a production machine began making unusual noises, leadership didn’t simply ignore it indefinitely because repairs would cost money. They understood that delaying preventive maintenance could eventually halt an entire production line. The repair would always cost more than the maintenance. Cybersecurity operates under the exact same principle today. The difference is that modern operational machinery is digital.
Instead of a broken conveyor belt, companies now face ransomware events, extended outages, regulatory scrutiny, failed audits, delayed acquisitions, lost customers, and rising insurance premiums.
The underlying business lesson, however, hasn’t changed at all. Deferred maintenance eventually becomes expensive maintenance.
One of the clearest examples of this is cyber insurance.
For years, many organizations viewed cyber insurance as a routine renewal process. Complete a questionnaire, submit basic information, pay the premium, and move on. But that world is disappearing quickly.
Insurance carriers are becoming increasingly aggressive in evaluating operational maturity before extending coverage. They now examine whether organizations have implemented multifactor authentication, modern endpoint protections, reliable backup strategies, identity controls, and disciplined patch management practices.
Organizations that fail these tests often don’t realize the consequences until renewal season arrives…
Premiums increase. Deductibles rise. Coverage becomes narrower.
In some cases, ransomware protections are reduced, or removed entirely.
What many executives see as a cybersecurity issue increasingly becomes a financial issue.
The revenue side of the equation is equally concerning.
Many organizations spend enormous resources building sales pipelines, pursuing strategic partnerships, and competing for enterprise clients. Then procurement teams send security questionnaires, and suddenly, deals begin slowing down.
Potential clients want assurance that vendors can protect customer data. They want evidence of mature security controls, incident response planning, vendor risk programs, and operational resilience. Companies that cannot demonstrate those capabilities increasingly find themselves losing business opportunities they never anticipated losing.
In some industries, poor cybersecurity maturity is no longer simply a risk issue. It’s a revenue issue.
Companies like UpGuard and SecurityScorecard have grown rapidly because organizations now recognize that trust itself has become part of the sales process. Operational downtime creates another silent EBITDA killer. When most executives hear the term “cyber incident,” they often envision stolen data or ransom payments. But the larger cost is frequently operational paralysis.
When MGM Resorts International suffered a major cyber incident, the financial damage extended far beyond technical recovery. Hotel operations were disrupted. Customer experiences suffered. Revenue-generating systems were impacted.
Change Healthcare demonstrated something similar on an even broader scale, where cyber disruption quickly evolved into a business continuity crisis affecting providers, patients, and financial operations.
These incidents become expensive because businesses are built on operational continuity. When systems stop functioning, EBITDA suffers immediately.
The merger and acquisition space may be where this issue becomes most visible.
A company can appear highly profitable on paper showing strong revenue, healthy margins, and a positive growth trajectory. Then, the technical due diligence begins.
Suddenly, acquiring firms discover undocumented systems, unsupported infrastructure, fragmented identity environments, aging platforms, compliance concerns, and hidden remediation costs. Those projected synergies begin shrinking. The integration timelines expand. And those valuation conversations change.
What leadership teams assumed was a highly valuable business can quickly become a far more expensive acquisition.
In today’s market, technical debt increasingly behaves like financial debt. And buyers are paying closer attention.
What makes these issues particularly dangerous is that none of them typically arrive as a single catastrophic event. They emerge gradually…
- A little more insurance cost here.
- A delayed deal there.
- Unexpected consulting fees.
- Emergency infrastructure replacements.
- Customer frustration.
- Regulatory pressure.
- Lost operational time.
Individually, these costs may seem manageable. Collectively, they quietly erode profitability year after year.
This is where many security leaders make a critical communication mistake. They walk into boardrooms speaking in technical acronyms. Touting buzzwords such as Zero Trust, EDR, SIEM, XDR, and SASE.
Boards are not asking for alphabet soup. They want to understand operational resilience, valuation protection, business continuity, and EBITDA preservation. The most effective security leaders are the ones who translate technical risk into financial language executives immediately understand. The biggest cybersecurity event your company faces may never become a headline. It may simply be years of avoidable operational friction caused by decisions that seemed financially responsible at the time.
Those delayed upgrades. The undocumented servers. The unsupported platforms. The weak identity controls. All of those ignored warning signs.
These decisions rarely create immediate panic. They simply reduce profitability little by little until leadership realizes they’ve been paying a hidden tax for years.
And by then… EBITDA has already been impacted.